How to Audit Azure Active Directory Logs for Suspicious Sign-Ins
In today’s cybersecurity landscape, identity is one of the most important security boundaries for any organization. As businesses increasingly rely on Microsoft 365, cloud applications, and remote access, protecting user accounts against unauthorized access has become a critical IT responsibility.
One of the most effective ways to identify potential identity-based attacks is by regularly reviewing authentication activity.
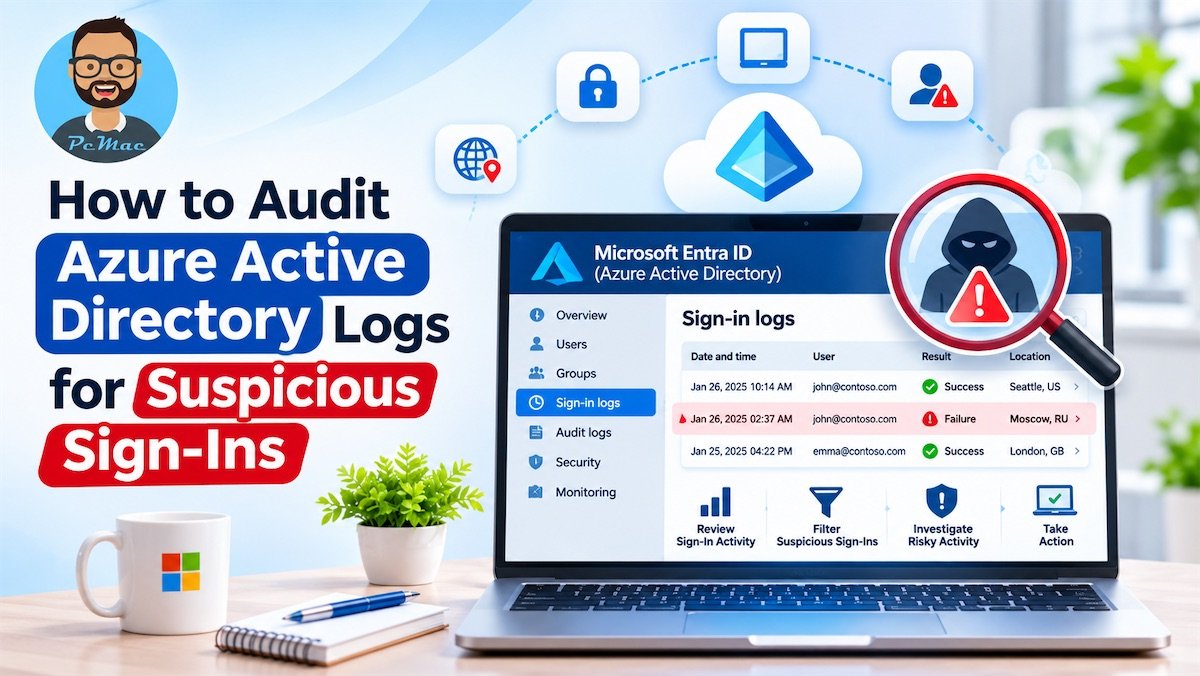
Knowing how to audit Azure Active Directory logs for suspicious sign-ins is an essential skill for IT administrators, Microsoft 365 administrators, and security analysts. By analyzing sign-in activity, administrators can identify unusual login locations, repeated authentication failures, suspicious IP addresses, and potentially compromised user accounts.
Microsoft has renamed Azure Active Directory (Azure AD) to Microsoft Entra ID. Although the product name has changed, administrators still commonly search for Azure AD sign-in logs when investigating authentication issues and potential security threats.
In this guide, you’ll learn how to access Microsoft Entra sign-in logs, investigate suspicious authentication activity, identify potential indicators of compromise, and configure automated monitoring using Azure Monitor and Log Analytics.
1. Understanding Azure Active Directory (Microsoft Entra ID) Sign-In Logs
- Before investigating suspicious authentication activity, it’s important to understand what information Microsoft Entra ID sign-in logs provide.
- Microsoft Entra sign-in logs record authentication attempts made against your organization’s tenant. They contain valuable information about who attempted to sign in, which application they accessed, where the request originated, and whether authentication succeeded or failed.
- Depending on the sign-in type, these records can also include device information, authentication methods, Conditional Access results, IP addresses, and risk-related information.
Types of Microsoft Entra Sign-In Logs
Microsoft Entra ID provides four primary sign-in log categories:
1. Interactive User Sign-Ins
Interactive sign-ins occur when a user actively participates in an authentication process.
Examples include:
- Entering a username and password.
- Approving an MFA authentication request.
- Using Windows Hello for Business.
- Completing an authentication challenge through Microsoft Authenticator.
These events are particularly useful when investigating suspicious user login attempts.
2. Non-Interactive User Sign-Ins
Non-interactive sign-ins occur when applications or operating system components authenticate on behalf of an already signed-in user without requiring another authentication prompt.
Examples include:
- Refresh token requests.
- Background authentication by Microsoft Office applications.
- Application session renewal.
- Single sign-on authentication processes.
These events are important because suspicious activity can occur through existing sessions or tokens without a new interactive password prompt.
3. Service Principal Sign-Ins
- Service principal sign-ins are authentication events performed by applications or automated services using their own identities rather than an individual user’s credentials.
- Administrators should monitor these events for unexpected application authentication, unfamiliar service principals, and unusual access patterns.
4. Managed Identity Sign-Ins
- Managed identity sign-ins are generated when Azure resources use managed identities to authenticate to supported services.
- Monitoring these events helps identify unexpected authentication activity involving applications and cloud infrastructure.
- Reviewing all four categories provides better visibility into identity-related activity across your Microsoft cloud environment.
2. Prerequisites for Accessing Azure AD Sign-In Logs
Before auditing sign-in activity, make sure your administrator account has the appropriate permissions and your organization has sufficient log retention.
Required Microsoft Entra Permissions
To view organization-wide sign-in logs, your account needs an appropriate Microsoft Entra role.
The following built-in roles are commonly used:
- Reports Reader: The least-privileged built-in role for viewing activity logs.
- Security Reader: Allows access to security-related information and reports.
- Security Administrator: Provides additional security management capabilities.
- Global Administrator: Provides broad administrative access but is generally unnecessary for routine log auditing.
For regular monitoring, assigning Reports Reader or another appropriately scoped least-privileged role is preferable to using a Global Administrator account.
Microsoft Entra Sign-In Log Retention
Microsoft Entra ID retains sign-in logs for different periods depending on the subscription.
| Microsoft Entra license | Sign-in log retention |
|---|---|
| Microsoft Entra ID Free | 7 days |
| Microsoft Entra ID P1 | 30 days |
| Microsoft Entra ID P2 | 30 days |
Risky sign-in reports have separate retention periods, so administrators should check the applicable retention requirements for each report type.
If your organization needs to retain authentication records for several months or years, configure diagnostic settings to export the logs to an Azure Monitor Log Analytics workspace, Azure Storage account, or Event Hub.
This is particularly important for organizations with regulatory, security investigation, or compliance requirements.
3. How to Audit Azure Active Directory Sign-In Logs in the Microsoft Entra Portal
The Microsoft Entra admin center provides a centralized interface for reviewing and investigating authentication events.
Follow these steps to access your organization’s sign-in logs.
Step 1: Sign In to the Microsoft Entra Admin Center
Open the Microsoft Entra admin center:
Sign in using an administrator account that has at least the Reports Reader role.
Step 2: Navigate to Sign-In Logs
From the Microsoft Entra admin center:
- Open Entra ID.
- Navigate to Monitoring & health.
- Select Sign-in logs.
You should now see authentication activity recorded for your organization’s tenant.
Step 3: Filter Failed Sign-In Attempts
Failed authentication attempts can provide useful clues about password spraying, brute-force attempts, and other suspicious activity.
To investigate failed logins:
- Open the sign-in logs page.
- Locate the Status filter.
- Select Failure.
- Choose an appropriate date range.
- Apply additional filters such as username, application, or IP address.
Look for repeated authentication failures involving the same account, multiple accounts accessed from one IP address, or unusual login activity outside normal working hours.
Remember that failed sign-ins can also result from incorrect passwords, expired credentials, or Conditional Access restrictions. Investigate the failure reason before treating an event as malicious.
Step 4: Investigate Individual Sign-In Events
Select an individual sign-in event to open its details.
Pay particular attention to the following information:
- User: The account attempting authentication.
- Application: The application being accessed.
- IP Address: The originating network address.
- Location: The approximate geographic location associated with the IP.
- Device Information: Browser, operating system, and device compliance details.
- Authentication Details: Authentication methods and MFA results.
- Conditional Access: Whether applicable access policies succeeded or failed.
- Sign-In Status: Whether authentication succeeded, failed, or was interrupted.
- Correlation ID: An identifier useful for troubleshooting and connecting related events.
These details help establish whether the authentication attempt matches the user’s normal behavior.
Step 5: Compare Sign-In Activity Over Time
Do not investigate suspicious authentication events in isolation.
Compare recent sign-in activity against the user’s historical behavior.
For example, investigate situations where:
- An employee normally signs in from one country but suddenly authenticates from another.
- A user generates hundreds of failed login attempts.
- A successful login follows repeated authentication failures.
- An unfamiliar application suddenly accesses sensitive resources.
- A previously inactive account begins generating frequent authentication events.
Combining multiple indicators provides a more reliable basis for identifying suspicious activity.
4. How to Identify Suspicious Sign-Ins and Indicators of Compromise
The most important part of auditing Azure AD logs is recognizing authentication patterns that could indicate an account compromise.
Here are some common warning signs security administrators should investigate.
4.1 Impossible Travel and Unusual Geographic Locations
Impossible travel refers to authentication activity originating from geographically distant locations within a period that makes normal physical travel unlikely.
For example, an employee successfully signs in from New York and then generates another successful sign-in from London only a few minutes later.
This could indicate stolen credentials, compromised sessions, or unauthorized account access.
However, geographic location data is not always accurate. VPN services, corporate proxies, mobile networks, and cloud infrastructure can make legitimate sign-ins appear to originate from unexpected locations.
Recommended investigation:
- Compare the IP addresses of both authentication events.
- Review the timestamps and authentication methods.
- Check whether the user was connected to a corporate VPN.
- Examine device and browser information.
- Review any associated Microsoft Entra Identity Protection risk detections.
Do not classify a login as malicious based on geographic location alone.
4.2 Unfamiliar IP Addresses and Anonymous Networks
Unexpected authentication requests from unfamiliar IP addresses deserve investigation, especially when they originate from known malicious infrastructure or anonymous proxy networks.
Pay particular attention to:
- IP addresses associated with known threat activity.
- Unexpected hosting provider or cloud infrastructure addresses.
- Anonymous proxy and Tor network connections.
- Repeated authentication attempts from the same source.
- IP addresses accessing multiple employee accounts.
Compare suspicious IP addresses against reputable threat intelligence sources and your organization’s known network ranges.
An unfamiliar IP address does not automatically indicate an attack, but it can provide an important investigation lead.
4.3 Repeated Authentication Failures Followed by Success
Password spraying and credential stuffing are common identity-based attacks.
During password spraying, attackers attempt a small number of commonly used passwords against multiple user accounts.
Credential stuffing involves testing previously exposed username and password combinations against other services.
Common warning signs include:
- Multiple failed login attempts against different users.
- Repeated failures from one IP address.
- Authentication attempts targeting privileged accounts.
- Successful sign-ins following a series of suspicious failures.
- Unusual authentication patterns across multiple applications.
If you identify this pattern, investigate the affected accounts, IP addresses, authentication methods, and related sign-in events.
4.4 Unfamiliar Devices and Applications
An unexpected device or application accessing corporate resources can indicate compromised credentials or unauthorized access.
Review device details for:
- Unrecognized operating systems.
- Unfamiliar browsers.
- Unexpected device identifiers.
- Devices that are not managed or compliant.
- Applications that users do not normally access.
Also investigate unusual service principal sign-ins and application permissions when an unfamiliar application appears to access corporate resources.
4.5 Suspicious MFA Activity
Multi-Factor Authentication provides additional protection, but attackers may attempt to manipulate users into approving fraudulent authentication requests.
Watch for:
- Unexpected MFA approval requests.
- Repeated authentication prompts.
- Unusual MFA method changes.
- Authentication attempts from unfamiliar devices.
- Successful authentication following suspicious MFA activity.
Microsoft Entra Identity Protection includes detections for certain suspicious MFA authentication scenarios, depending on licensing and configuration.
5. Automate Suspicious Sign-In Detection Using Microsoft Entra ID Protection
Manually reviewing authentication logs is useful during investigations, but it is not a practical way to monitor a large organization continuously.
Microsoft Entra ID Protection helps organizations identify potentially compromised users and risky authentication activity using Microsoft’s identity threat detection capabilities.
It evaluates different signals and generates risk detections that administrators can investigate.
Understanding Sign-In Risk and User Risk
Microsoft Entra ID Protection provides two important risk concepts.
Sign-In Risk
- Sign-in risk indicates the likelihood that a particular authentication request was not performed by the legitimate account owner.
User Risk
- User risk indicates the likelihood that an account has been compromised.
- Depending on the detection, risk levels can include Low, Medium, and High.
Recommended Identity Protection Practices
Administrators should consider the following security measures:
- Review risky sign-ins regularly.
- Investigate users identified as high risk.
- Configure Conditional Access policies based on sign-in risk where licensed.
- Require MFA when appropriate.
- Require secure password changes or account remediation for compromised users.
- Review risk history to understand recurring suspicious activity.
Some advanced risk detections and automated risk-based Conditional Access capabilities require Microsoft Entra ID P2 licensing or other applicable subscriptions.
Always verify the licensing requirements for individual detection types before designing your security policies.
6. Export Azure AD Sign-In Logs to Azure Monitor and Log Analytics
The default Microsoft Entra log retention period may not be sufficient for organizations that need long-term security monitoring.
To maintain a longer authentication history, administrators can configure diagnostic settings to export sign-in logs to Azure Monitor.
Step 1: Open Diagnostic Settings
- Sign in to the Microsoft Entra admin center.
- Navigate to Entra ID > Monitoring & health.
- Open Diagnostic settings.
- Select Add diagnostic setting.
Step 2: Select Sign-In Log Categories
Choose the sign-in log categories you need to monitor.
Depending on your requirements, these may include:
- SignInLogs
- NonInteractiveUserSignInLogs
- ServicePrincipalSignInLogs
- ManagedIdentitySignInLogs
- RiskyUsers
- UserRiskEvents
Available categories depend on the tenant and supported diagnostic configuration.
Step 3: Configure the Destination
Select Send to Log Analytics workspace and choose the appropriate Azure subscription and workspace.
You can also configure other supported destinations, such as Azure Storage or Event Hub.
Step 4: Save and Verify
Save the diagnostic settings and verify that sign-in events are arriving in the selected destination.
Once the data is available, administrators can use Kusto Query Language (KQL) to investigate authentication patterns.
Example KQL Query: Find Failed Sign-In Attempts
The following query identifies failed interactive user sign-ins in the last 24 hours.
SigninLogs
| where TimeGenerated >= ago(24h)
| where ResultType != "0"
| summarize FailedAttempts = count()
    by UserPrincipalName, IPAddress, ResultDescription
| order by FailedAttempts desc
Example KQL Query: Identify Multiple Failed Attempts From One IP
SigninLogs
| where TimeGenerated >= ago(24h)
| where ResultType != "0"
| summarize
    FailedAttempts = count(),
    TargetedUsers = dcount(UserPrincipalName),
    Users = make_set(UserPrincipalName, 10)
    by IPAddress
| where FailedAttempts >= 10
| order by FailedAttempts desc
These queries are starting points for investigation, not automatic proof of malicious activity. Adjust thresholds to match your organization’s normal authentication patterns.
Why Log Analytics matters: It allows security teams to search historical authentication activity, correlate events, build dashboards, and create detection rules for suspicious sign-in patterns.
7. Establish a Regular Azure AD Sign-In Log Auditing Process
A successful identity security strategy requires more than configuring logging and occasionally reviewing suspicious events.
Organizations should establish a repeatable monitoring and incident response process.
Here are some recommended practices:
1. Review failed sign-ins regularly
- Monitor repeated authentication failures and investigate unusual patterns.
2. Monitor privileged accounts
- Pay particular attention to Global Administrators, Security Administrators, and other accounts with elevated permissions.
3. Enable MFA and Conditional Access
- Require strong authentication and use device or risk-based access controls where appropriate.
4. Monitor service principal activity
- Review application authentication and investigate unexpected changes in application behavior.
5. Retain authentication logs
- Export logs to Log Analytics or another supported destination when longer retention is required.
6. Investigate Identity Protection alerts
- Review risky users, risky sign-ins, and relevant risk detections.
7. Establish an incident response procedure
- Define how administrators should disable compromised accounts, revoke sessions, reset credentials, and investigate related activity.
8. Review audit logs alongside sign-in logs
- Sign-in logs show authentication activity, while audit logs help identify changes to users, groups, applications, and other tenant resources.
Reviewing both provides a more complete picture of suspicious identity activity.
Frequently Asked Questions About Azure AD Sign-In Logs
1. How do I check Azure Active Directory sign-in logs?
- Sign in to the Microsoft Entra admin center at https://entra.microsoft.com/. Navigate to Entra ID > Monitoring & health > Sign-in logs. You can filter authentication events by user, application, status, IP address, and date range.
2. What is the difference between Azure AD audit logs and sign-in logs?
- Sign-in logs record authentication events, including successful and failed login attempts. Audit logs record administrative and directory changes, such as user creation, group membership changes, application updates, and permission modifications.
3. How long does Microsoft Entra ID retain sign-in logs?
- Microsoft Entra ID Free retains sign-in logs for 7 days, while P1 and P2 subscriptions retain them for 30 days. Organizations requiring longer retention should export logs to Azure Monitor, Log Analytics, Azure Storage, or another supported solution.
4. How can I identify suspicious login attempts in Azure AD?
- Look for repeated failed authentication attempts, unexpected IP addresses, unfamiliar devices, unusual geographic locations, suspicious MFA activity, and successful sign-ins following multiple failures. Investigate the full authentication context before determining whether an account has been compromised.
5. Can I export Azure AD sign-in logs to Excel?
- Yes. Administrators can download sign-in activity from the Microsoft Entra admin center in supported formats, including CSV. This makes it easier to perform offline analysis and share investigation data with authorized security personnel.
6. What permissions are required to view Microsoft Entra sign-in logs?
- Reports Reader is the least-privileged built-in Microsoft Entra role required to access activity logs. Security Reader and appropriately privileged administrative roles can also provide access.
7. What is Microsoft Entra ID Protection?
- Microsoft Entra ID Protection is an identity security capability that detects and helps investigate potentially compromised accounts and risky authentication activity. It provides risk detections and supports risk-based remediation, with some advanced capabilities requiring Microsoft Entra ID P2 licensing.
Conclusion
Knowing how to audit Azure Active Directory logs for suspicious sign-ins is an essential part of protecting modern cloud environments.
Microsoft Entra ID provides valuable authentication telemetry that allows administrators to investigate failed login attempts, unfamiliar locations, suspicious IP addresses, unusual device activity, and potentially compromised accounts.
By regularly reviewing interactive and non-interactive sign-ins, monitoring service principal activity, using Microsoft Entra ID Protection, and exporting authentication records to Azure Monitor, organizations can build a more effective identity monitoring strategy.
The key is to combine regular log reviews with automated detection, appropriate Conditional Access policies, and a clearly defined incident response process.
A proactive approach to Microsoft Entra sign-in log auditing helps security teams identify suspicious activity earlier, investigate potential account compromises, and strengthen the overall security of their Microsoft 365 and cloud environments.
Official Microsoft references to include
These are authoritative resources that support the technical instructions in the article: